How AI-Powered Decisions Can Enhance the Insurance Value Chain
Prepare your insurance value chain to use the next two waves of AI — powered automation and decision-making.
Audits verify compliance. Assurance services who whether your systems and controls work. Both matter to IT and security leaders who answer to regulators, boards and customers.
The terms “audit” and “assurance” — like “privacy” and “security,” “agreement” and “contract,” or “authentication” and “authorization” — are often used interchangeably. But audit and assurance are two different concepts.
An audit verifies that your systems and records are accurate and compliant. Assurance services build confidence in how well those systems work.
This distinction sounds relatively simple. However, understanding the difference between audit and assurance services can help solve complex business problems, such as meeting compliance regulations and mitigating cyberthreats.
Let’s examine the differences between audit and assurance and consider how they can strengthen your business together.
An audit is a systematic examination of systems, records or processes.
The audit’s primary objective is to verify records’ accuracy and ensure an organization complies with relevant regulations and accepted standards. In many cases, an audit verifies compliance with externally established standards. However, it can also be used to ensure an organization complies with its own internal governance requirements.
A prime use case for audits is verifying the integrity of financial records, whether for an external body, such as the Internal Revenue Service (IRS), or internal stakeholders, including your company’s chief financial officer or accounting department.
Audits tend to follow predefined frameworks, such as those outlined by ISACA, the Institute of International Auditors (IIA), or the American Institute of CPAs and Chartered Institute of Management Accountants (AICPA & CIMA), all of which are designed to help organizations meet industry standards. Some of these include:
Because they’re based on these and similar standards, audits can go a long way toward reassuring internal stakeholders and compliance officials of your operations’ safety and quality. However, by engaging assurance services, you can earn confidence at an even deeper level.
Assurance services are broader than audits because they encompass more than verifying accuracy or compliance. While assurance services often include auditing, assurance goes a step further.
When a company engages assurance services, the goal is to build confidence. In most cases, an assurance process is designed with a specific audience in mind and aims to give those stakeholders confidence in data’s integrity and the efficacy of systems or processes.
Investors, for instance, may require assurance reports to make sure that financial practices and operational systems justify a stock or share price. In some countries, regulatory bodies that enforce environmental, social, and governance (ESG) standards may specifically ask for an assurance report. For example, they may want to make sure that greenhouse gas emissions or hiring practices meet their standards, and an assurance report details the extent to which this is true.
One of the most common types of assurance reports are those that detail cyber defense mechanisms.
For example, suppose you’re in charge of cybersecurity for a software-as-a-service (SaaS) company. You may engage an assurance provider, who will then conduct a six-month Security Operating Center (SOC) 2 attestation. But that attestation is only a single step in the assurance process.
The assurance provider would also evaluate the reliability of your cyber defenses, including checking the health and shelf life of physical equipment such as routers and firewalls. The provider would further verify that you have the most up-to-date cyber controls in place, not just those that satisfy SOC 2 requirements.
The assurance process may also review your internal governance protocols to make sure they promote transparency among the IT team, managers, and the C-suite regarding how cyber incidents are monitored, mitigated and reported.
Ultimately, your assurance provider generates a report. You can present this report to the rest of the cyber team, the IT team, the C-suite, and, especially, investors concerned about your digital defenses’ efficacy.
Any organization that needs to demonstrate compliance and quality to specific groups of stakeholders should pursue assurance rather than basic auditing only.
This is particularly true of companies in highly regulated industries, including:
Assurance plays an integral role in mitigating risk and demonstrating risk reduction to internal managers and insurance companies. By hiring assurance providers, you remove the guesswork for risk assessors by giving them concrete, quantifiable breakdowns of how you’re reducing risk exposure.
For example, when negotiating the cost of a cybersecurity rider with an insurance company, an assurance report can demonstrate why your premium should be lower than their normal rates. Perhaps you’ve gone beyond satisfying the SOC 2 attestation standards, and you feel this drastically reduces your risk of cyber incidents. An assurance report could use straightforward evidence to demonstrate why this is true.
Although audit and assurance services have distinct roles, they can be easily confused or conflated. Here’s a breakdown of what makes them different from each other.
No. Audits focus on accuracy and compliance, while assurance focuses on building confidence.
Audit vs. Assurance at a Glance
| Audit | Assurance | |
| Purpose | Verifies accuracy and compliance | Builds confidence that systems and controls work |
| Question it answers | Do we meet the standard? | Can stakeholders trust how we manage risk? |
| Common frameworks | GAAP, ISO, NIST | SOC 2 attestation, HIPAA risk assessment |
| Typical audience | Regulators, compliance officials, internal stakeholders | Boards, investors, customers, insurers |
| Cybersecurity example | A NIST audit confirms defenses are in place | An assurance review tests whether those defenses hold up |
For example, a GAAP audit would verify that an accounting department is adhering to Generally Accepted Accounting Principles. But an assurance process would go a step further. It may demonstrate that applying GAAP standards has reduced the risk of overspending on overhead.
Assurance services may also show how the reliability of an organization’s accounting system has improved over time not just by using GAAP but also by implementing automatic reports around cash flow, inventory levels, and debt-to-income ratios.
Understanding the differences is one thing, but knowing which option to choose can bring its own challenges. Here are some guidelines that can make the choice more straightforward.
The answer is usually both. Compliance pressure is part of the reason. In ISACA’s 2026 Tech Trends & Priorities Pulse Poll of nearly 3,000 cybersecurity, IT audit, and governance professionals, 66 percent named regulatory compliance as their organization’s top focus area for 2026.
Every organization that must meet compliance regulations will need at least one type of audit and, in most cases, an assurance engagement will also bring value because it demonstrates the effectiveness of its systems.
Additionally, if a regulatory body requires an assurance report in addition to an audit, you must provide it as well.
In certain situations, an assurance engagement is sufficient. For example, a utility may need to generate an assurance report to present at a town meeting. Or a healthcare company may need to produce an assurance report, such as a Health Insurance Portability and Accountability Act (HIPPA) risk assessment, to demonstrate to the board of directors that their system for protecting patient privacy has been, and will continue to be, effective.
You can use the decision matrix below to help you determine whether your organization needs an audit, assurance engagement, or both:
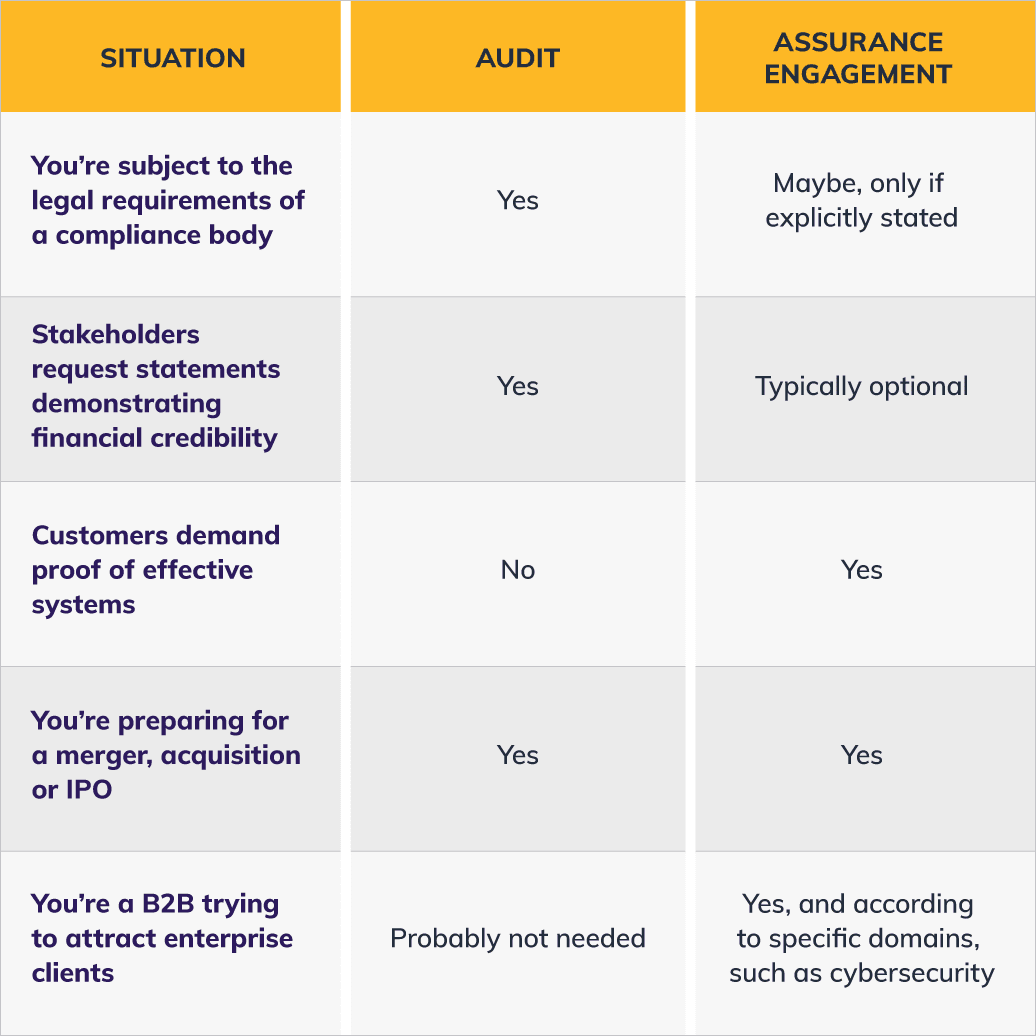
While each solution offers unique benefits, understanding how to use audits and assurance services together can help you develop a more comprehensive risk mitigation system.
An audit always provides some level of assurance simply because it demonstrates that an organization’s system checks the right boxes. If your company passes an International Financial Reporting Standards (IFRS) audit, for example, stakeholders can be assured that you have statements in place regarding cash flow, equity and income.
Audits and assurance services often work together because an assurance report frequently requires an audit. This means that an audit is, in many cases, the first step in providing assurance because it serves as a building block for an assurance program.
When used together, audits and assurance engagements support a general risk management program by providing a combination of data and analysis to certify your organization is using best practices. They also build trust with stakeholders because they show you’ve put systems in place to reduce risk.
At the same time, it’s possible to get an assurance report without performing an audit. For instance, a financial services company can engage with assurance services to demonstrate how effective their collections processes are. This wouldn’t require an audit.
Audits and assurance can be powerful tools when making strategic decisions. For example, an audit may reveal that an insurance company uses best practices when tracking accounts receivable, but an assurance report may show that collections processes aren’t effective. Using this information, the insurance company may invest in training employees around collections best practices or purchase software that comes with effective collections frameworks.
IT audit and assurance have had to adjust as cyberthreats have become a ubiquitous element of risk management. The cost of getting it wrong is rising. The global average cost of a data breach climbed to $4.99 million in IBM’s 2026 Cost of a Data Breach Report, up from $4.44 million in 2025. Audit and assurance services have grown to meet this challenge.
For instance, audit and assurance services now:
Many industry leaders now recognize the benefits of using audit and assurance services. Let’s explore a real-world example next.
FreshBooks, a provider of cloud-based accounting software, benefited from audit and assurance services by conducting payment card security decision system support ( PCI DSS) audits and engaging with credit card security assurance services.
FreshBooks undergoes regular audits with a third-party auditor to confirm it remains PCI DSS compliant. The combination of advanced auditing and assurance services has resulted in automated systems designed to prevent attackers from stealing sensitive information.
For instance, if a customer types a card number into a field not meant for payment data, such as invoice notes, the system automatically redacts it. In this way, FreshBooks reduces the risk of attackers intercepting sensitive information and either using it to steal money or selling it on the dark web. Evidence that a control like this keeps working is what an assurance engagement delivers.
Like FreshBooks, your organization can yield the fruit of risk-reducing audits and assurance services. The key is to be clear about your needs and goals.
When it comes to audits and assurance engagements, you must know what you’re asking for. An audit checks, and assurance assures. You can use both to enhance your operations, establish trust, and mitigate risk.
The future of risk mitigation will combine audit and assurance services and include:
At Centric Consulting, our audit and assurance services take it a step further: We use audit data to guide you through the process of improving your systems. To achieve this, we identify gaps and inefficiencies. We then help you address them by implementing internal controls. We also bring in regulatory experts to help you navigate standards like HIPAA, Sarbanes-Oxley (SOX), and Federal Financial Institutions Examination Council (FFIEC). That work spans risk and maturity assessments, control testing, compliance audits and assurance, and audit response and remediation.
Our experts identify the most effective solution using a vendor-neutral approach. We provide unbiased recommendations built around what will help your organization meet its goals.
Our cybersecurity audit and assurance experts provide you with whatever you need to meet compliance requirements and build trust with a range of stakeholders. Learn more by connecting with Centric today. Let’s Talk